Subscribe to real-time event streams, receive instant HTTP notifications, and verify HMAC-SHA256 signatures.
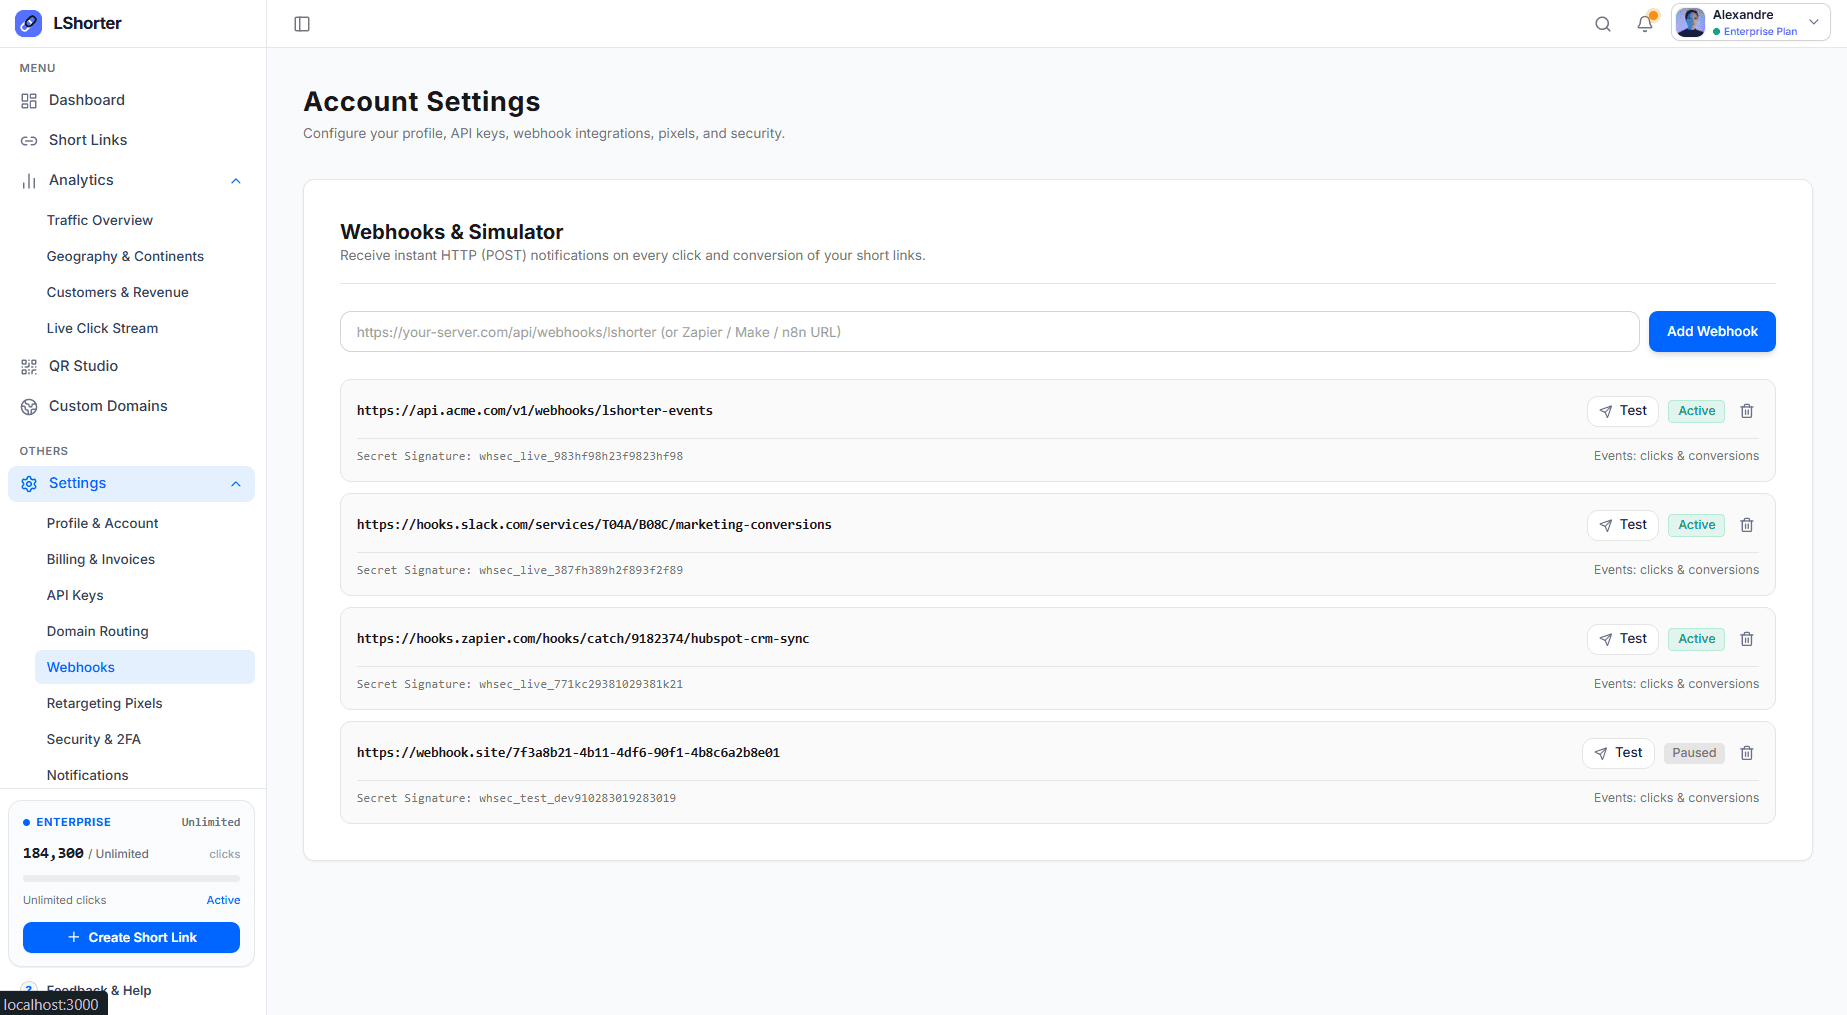
LShorter webhooks notify your backend systems in real time whenever an event occurs on your short links (click registered, conversion recorded, quota reached, link expired).
All outgoing HTTP POST payloads are cryptographically signed with an HMAC-SHA256 secret key via the x-lshorter-signature header to guarantee authenticity and prevent tampering.
Pour des raisons de sécurité et d'intégrité, la création et la configuration des webhooks s'effectuent exclusivement depuis le tableau de bord web LShorter (Paramètres > Webhooks). L'API et le SDK vous permettent de lister vos abonnements actifs et de traiter les événements entrants.
Core architectural pillars ensuring high performance, isolation, and security.
Ready-to-use TypeScript code snippets and configuration examples for your integrations.
Cryptographically verify incoming webhook payloads before processing:
Direct HTTP request methods, parameters schema, authentication, and responses.
Retrieves all active webhook subscriptions configured for your account. (Note: New webhooks must be registered securely from the LShorter Web Dashboard in Settings > Webhooks).
JSON payload dispatched on a link.clicked or link.converted event:
Expert tips to maximize performance, resilience, and link security.
Respond quickly with an HTTP 200 OK (within 3,000ms) and offload lengthy business tasks to background queues (BullMQ, Celery, SQS).
Always verify the HMAC-SHA256 signature before parsing or acting upon webhook JSON data.
Store received event.id tokens to build idempotent event handlers that safely handle network retries.